Risk Assessment vs. Transaction Monitoring: Why Your BSA/AML Program Needs Both
Most BSA officers could define the difference between a risk assessment and transaction monitoring in their sleep. Yet in practice the two get treated as interchangeable, and that is where programs start to drift.
On October 8, RiskRator hosted a panel with Andrea Valentin, Chief Risk Officer at Maxwell State Bank, and Cody J. Smith, CPAML, Managing Director of CSMB International and RiskRator’s Chief Product Officer. Their argument was simple: the two disciplines are complementary, not interchangeable, and a program is only as strong as the connection between them. Watch the full webinar replay.
The flashlight and what it finds
Andrea offered the cleanest way to hold the distinction:
“A risk assessment is going to tell you where to point your flashlight. Transaction monitoring is going to tell you what you found when you did.”
The risk assessment is strategic. It asks where the institution is exposed across its customers, products and services, delivery channels and geography, and it gives the board and senior management the risk profile they need to approve the program and direct resources.
Monitoring is tactical. It applies rules and thresholds to transactions and produces alerts, investigations and, when warranted, SARs.
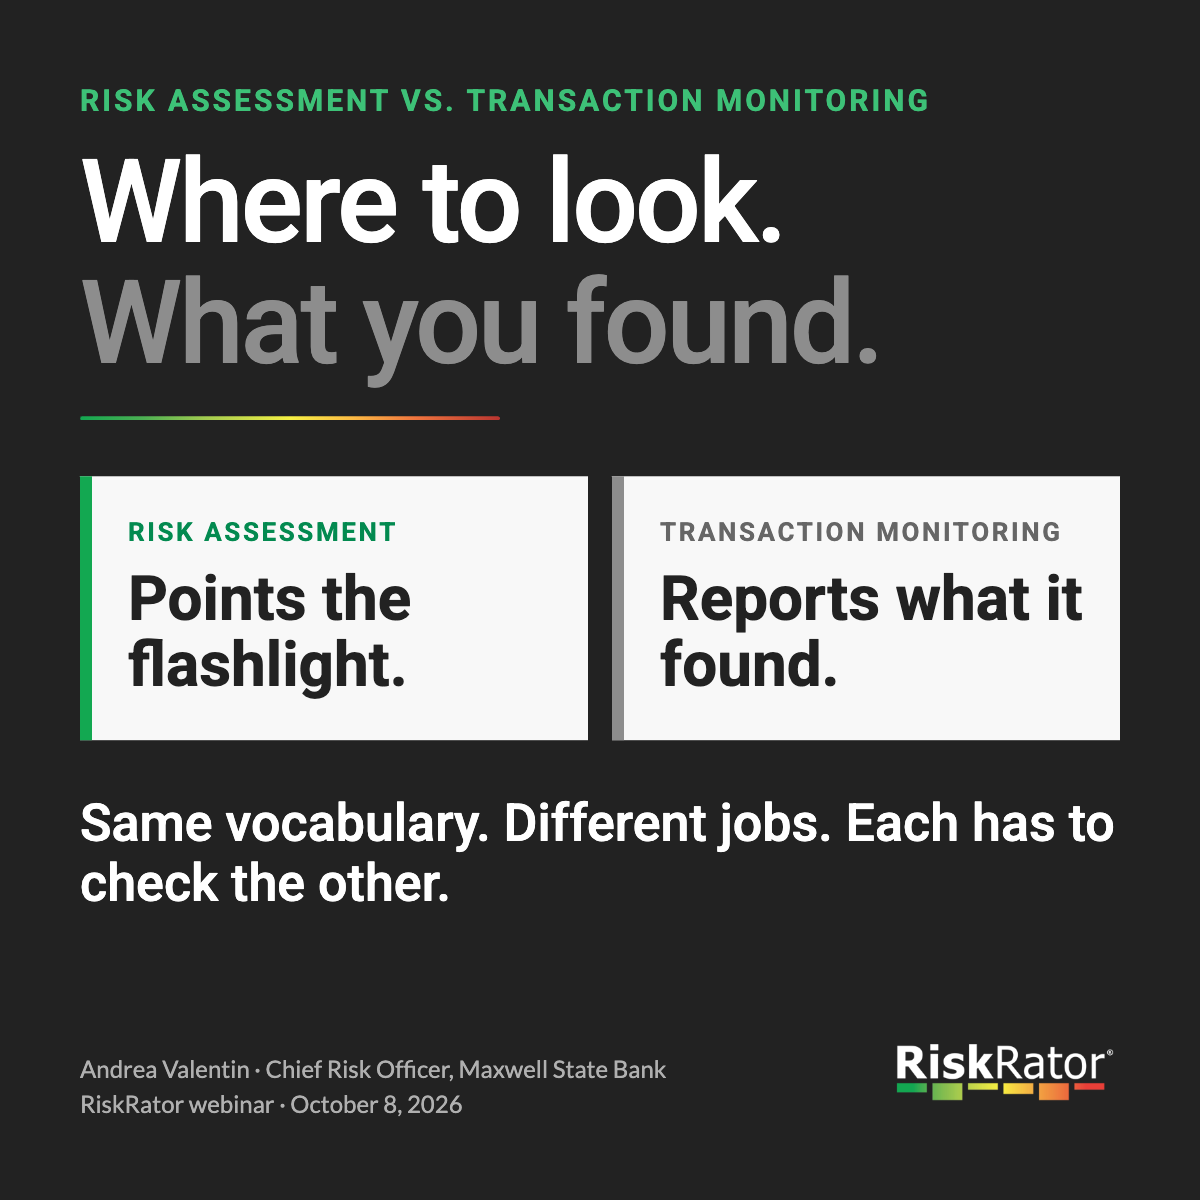
The confusion, Andrea noted, comes partly from vocabulary. Both functions talk about risk, scores and thresholds, so it is easy to answer one question with the other function’s output. Customer risk scores are a common example. They are an input to the risk assessment, not the assessment itself.
The risk assessment comes first, and it never stops
Cody described the risk assessment as the blueprint for the whole program. A risk-based program cannot be designed until you know where the risk lies. But a blueprint that never changes stops describing the building.
That is why the assessment has to be a living document. The FinCEN AML/CFT Program Rule proposed on April 7, 2026, would make the risk assessment a required, examinable element of every program. The Federal Reserve’s parallel proposal goes further on timing: it would require the assessment to be updated promptly upon any change that significantly alters the bank’s risk profile. Both rules are still proposed, but the direction is clear. An annual snapshot is no longer the standard examiners will measure against.
The feedback loop is the test
The two functions connect through a loop that most programs describe and few actually run:
- The risk assessment identifies where risk sits.
- Rules and thresholds are tuned to that risk.
- Monitoring produces alerts.
- Alerts become investigations.
- Investigations become SARs.
- SAR patterns are analyzed against the risk assessment, and the assessment is updated.
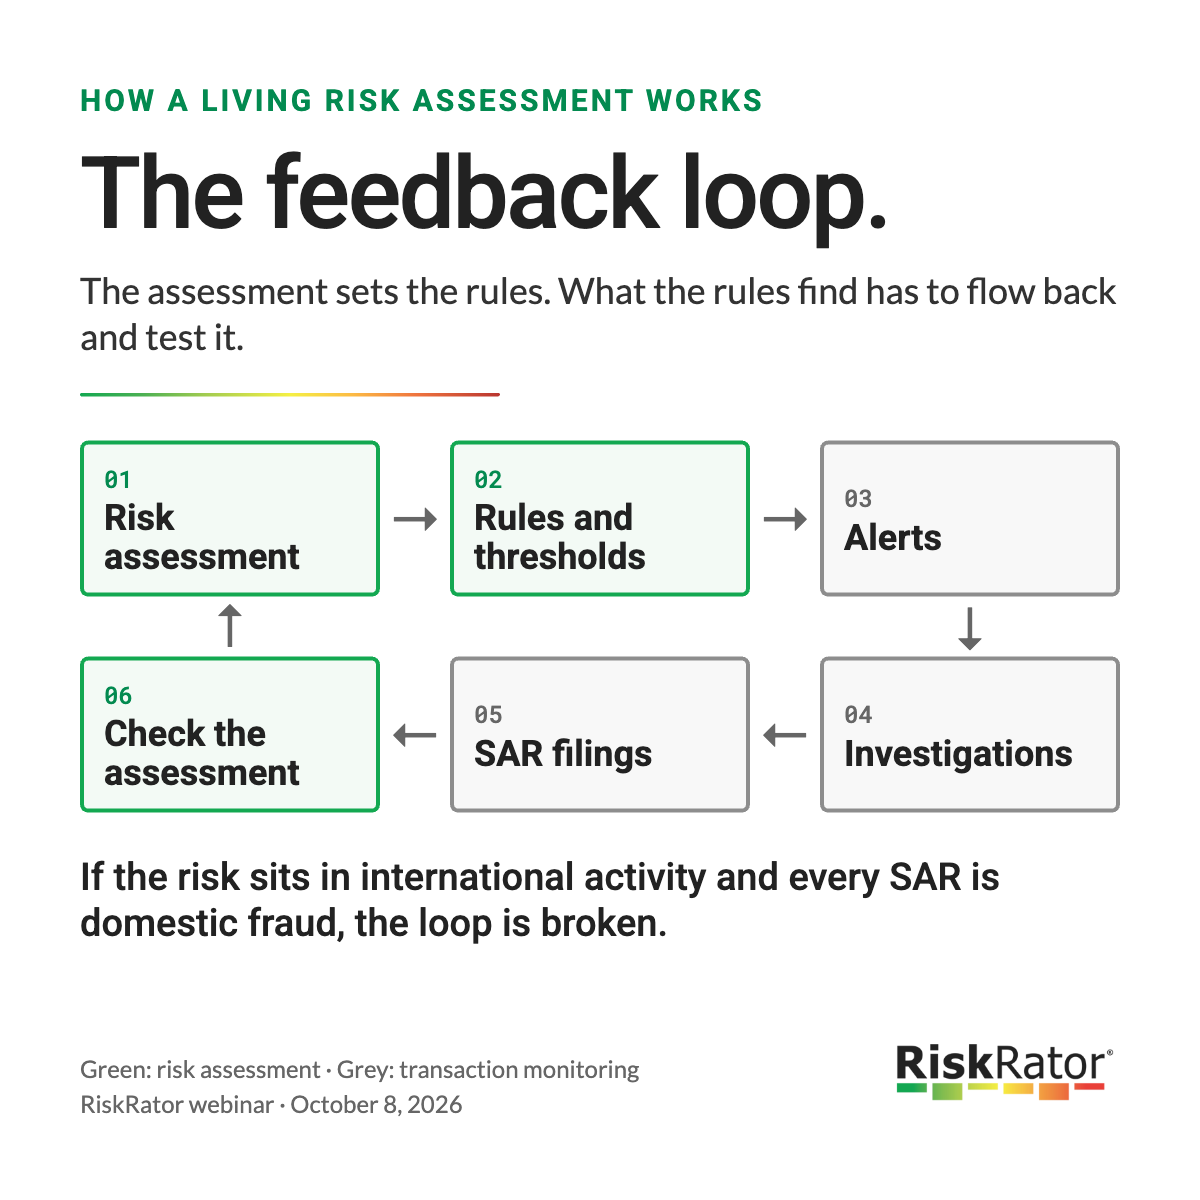
The sixth step is where the loop usually breaks. Cody’s test for it is blunt: if your risk assessment says your exposure sits in international transactions and every SAR you file is domestic fraud, something is disconnected. Either the risk is misrepresented, monitoring is miscalibrated, or both.
The practical version is a regular review of a few numbers: how many alerts become investigations, how many investigations become SARs, and what typologies those SARs actually describe. If those outputs do not line up with the risk assessment, that gap is the work.
What the room told us
We polled attendees on two questions. Asked how often they tune monitoring rules based on changes in their risk assessment, 60 percent said dynamically, as risk shifts. A quarter said annually, and about one in eight said rarely or never.
Asked which part of their program demands the most manual effort, 75 percent named clearing and investigating alerts. Only 13 percent named maintaining the risk assessment.
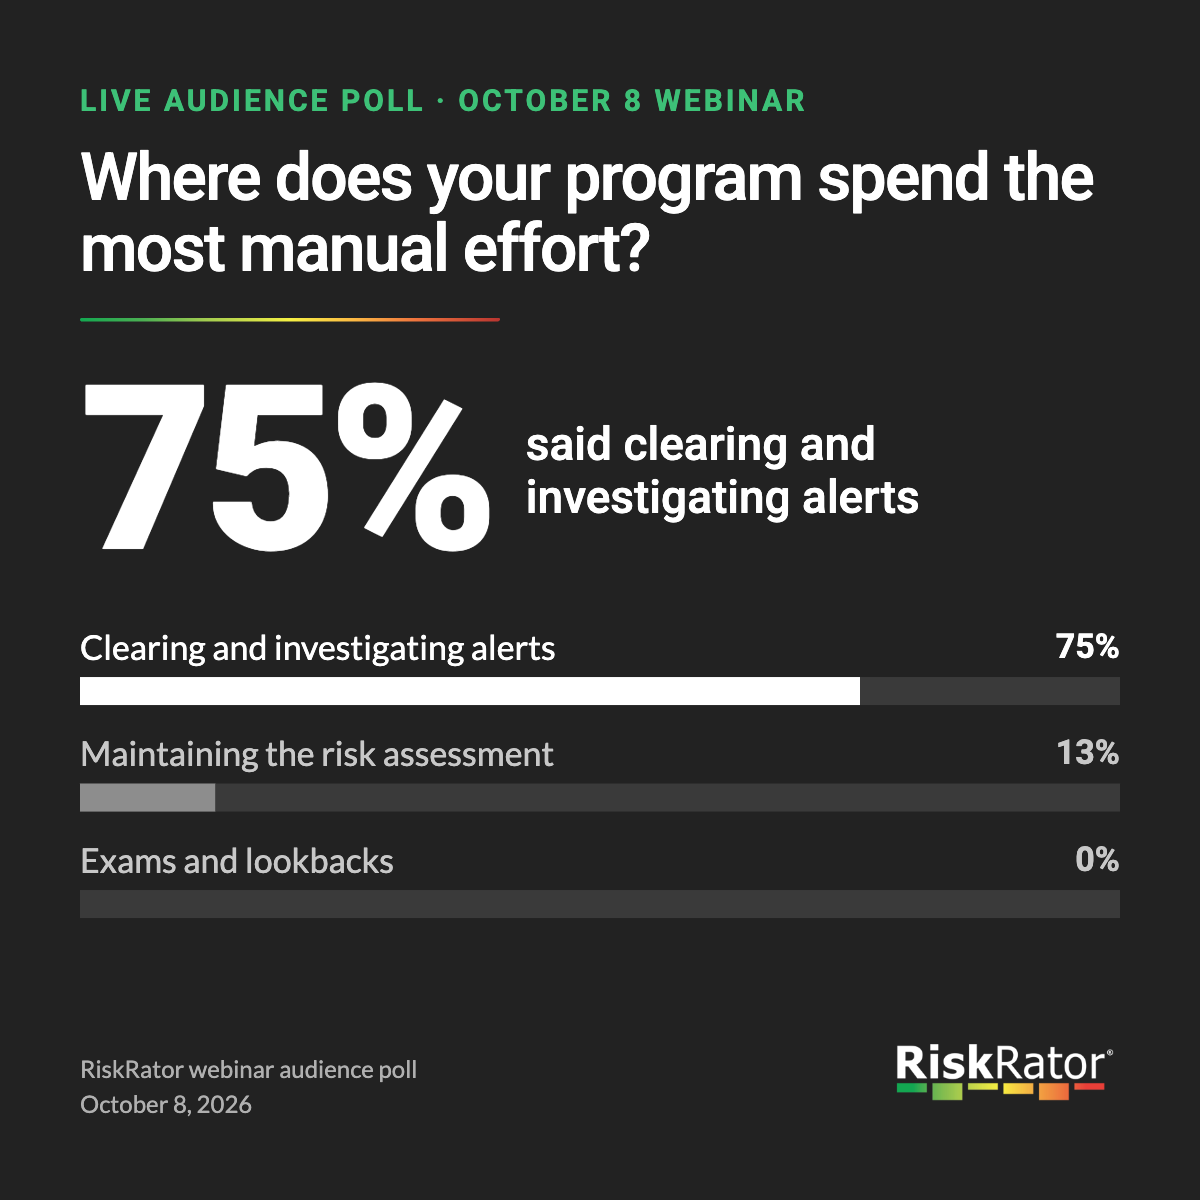
That second result is worth sitting with. The risk assessment is the input that decides whether those alert hours are spent in the right place. When it is stale, every downstream hour is calibrated to a bank that no longer exists.
Zero alerts is a question, not an answer
Andrea shared her own reassessment triggers: a new product or channel, a rule that produces zero alerts, and sharp swings in alert volume or false positive rates. The zero-alert trigger surprises people. A quiet rule may mean the activity is not there. It may also mean the rule is not looking where the risk actually is.
She added a standard every monitoring team should be able to meet: if you cannot tell the story behind a threshold, it is not good enough.
Automate the assembly, keep the judgment
The panel agreed on where automation belongs. Alert clearing and investigation should stay human; banks that auto-close alerts to save time keep showing up in enforcement actions. What should be automated is the assembly: pulling transaction, customer and product data into one place so a person can look at the institution’s risk strategically. For a recent example of what happens when that assembly fails, see the consent order case study in the webinar replay.
As Andrea put it in closing, a risk assessment should not take as many people to produce. It should take more thinking.
How RiskRator fits
RiskRator builds the bank-wide BSA/AML risk assessment from your own transaction data. A BSA officer exports a standard file from the core system, and RiskRator produces an institution-level risk profile that can be refreshed whenever the business changes. No integration project, and no waiting for next year’s cycle to see what moved.
Watch the full webinar replay · See how RiskRator works
Frequently asked questions
What is the difference between a BSA/AML risk assessment and transaction monitoring?
The risk assessment identifies where an institution is exposed to money laundering and terrorist financing risk across customers, products, channels and geography. Transaction monitoring applies rules to activity to detect potentially suspicious transactions. The assessment decides where to look; monitoring reports what it found.
Can transaction monitoring replace a risk assessment?
No. Monitoring output is an input to the risk assessment, along with customer risk ratings and the institution’s actual experience. Without an assessment, there is no basis for setting rules and thresholds.
How often should a risk assessment be updated?
At minimum on a set cycle, and whenever the risk profile changes: a new product, channel or partner, or a meaningful shift in monitoring results. The Federal Reserve’s proposed AML/CFT program rule would require prompt updates upon significant changes.
What does a feedback loop between the two look like?
SAR and alert patterns are reviewed regularly against the risk assessment. When filings concentrate in areas the assessment rates as low risk, either the assessment or the monitoring calibration needs to change.


Leave a Reply
Want to join the discussion?Feel free to contribute!